Contract Compliance
Risk Advisory and Assurance Services
Every organization faces risk – from cybersecurity threats and regulatory changes to gaps in internal controls and third-party dependencies. Managing these risks effectively requires more than a compliance checklist; it calls for a balanced approach to governance, oversight and resilience.
Our Risk Advisory and Assurance Offerings
Withum’s Risk Advisory and Assurance Services Team combines technical, operational and industry experience to help organizations evaluate exposures, implement strong controls and turn risk management into a business advantage. Our risk and compliance services support both proactive and ongoing needs, from cybersecurity readiness and SOC reporting to internal audit and compliance programs.
Withum offers a full range of risk and compliance services to help organizations identify, assess and address risks while supporting long-term strategic growth.
Cybersecurity Consulting
PCI Compliance
Systems and Organization Controls (SOC) Audit
Why Withum?
Withum’s Risk Advisory and Assurance Services Team combines decades of experience in cybersecurity, audit and compliance with a practical understanding of how businesses operate. We deliver clear, actionable guidance that helps leaders make informed decisions, protect enterprise value and strengthen governance structures.
Our advisors design risk consulting services that balance risk mitigation with business performance, helping mid-market companies and large enterprises adapt to evolving regulations while maintaining trust and long-term stability.
Connect with Our Leaders
Partner, Market Leader, Risk Advisory and Assurance Services
Princeton, NJ – Corporate Headquarters
Partner, Lead, Cybersecurity Consulting Services
Rochester, NY
Related Insights
Why Managed IT Is a Business Strategy, Not Just a Help Desk
For small and midsize businesses (SMBs), technology has become fundamental to nearly every part of the business, from serving customers and processing payments to managing data and keeping operations running. Yet many businesses still approach IT reactively, addressing issues when something breaks rather than managing technology as critical business infrastructure. Artificial intelligence is making that…
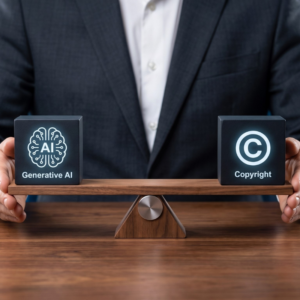
Regulatory Intervention and Artificial Inspiration: Examining Google’s AI Governance Proposal on Copyright Protections
Similar to other major AI developers, Google has been facing several lawsuits that challenge the tech giant’s alleged use of copyrighted materials to train its AI models. Against that backdrop, Google’s white paper on AI policy, A Pragmatic Approach to AI Governance in America, appears to present a balanced approach to facilitating continued innovation on…
How Oversight Gaps Can Develop in Multiemployer Plans
Even in well-run multiemployer plans (“Plans”), oversight gaps can quietly grow over time. In many cases, these gaps are not the result of negligent or disengaged Boards. Rather, they emerge when too much reliance is placed on existing systems, familiarity and routine reduce visibility into how processes actually operate, or technical complexity discourages questions and…
Contact Us
For more information or to discuss your business needs, please connect with a member of our team.